Air Traffic and Navigation Services in South Africa is probing a ransomware-linked malware breach in its operational technology network, with suspicions of data exfiltration and insider involvement threatening the security of a major portion of global airspace.
Malware tied to ransomware has slipped into the operational technology network at South Africa's Air Traffic and Navigation Services (ATNS). The company is now in crisis mode. Suspected data theft and possible insider help have forced a full-scale cyber-forensics investigation. ATNS is racing to understand the damage.
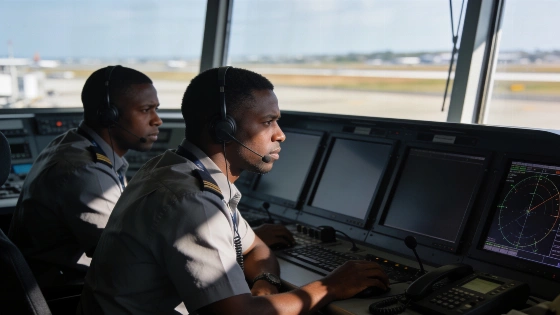
ATNS runs air traffic control and weather operations for about 10% of the world's airspace. The breach started with suspicious activity in OT systems that support weather services. Early checks found malware signatures linked to the first stages of ransomware attacks. This raised fears of both service disruption and stolen data. Internal ATNS documents, cited by independent security analysts, show the malware hit the OT segment that handles meteorological data integration. That system is crucial for flight safety and navigation.
Indagini su furto dati e ruolo interno
Initial findings point to data being sent to external IP addresses in China. That has made the breach look even worse. Investigators are focusing on two South African sites-Port Elizabeth Airport (FAPE) and possibly East London Airport (FAEL)-plus Maputo International Airport in Mozambique (FAMM). They are looking hard at whether someone inside helped steal the data. ATNS says its technical team has already contained the threat and removed the malware. But the company admits it needs outside digital forensics to fully trace the attack, measure the damage, and check for any leftover risks. This matches best practices from the Agenzia per la Cybersicurezza Nazionale (ACN), which call for third-party forensic checks after incidents in critical infrastructure.
ATNS says its team stopped the attack. Now, the company is bringing in outside cyber-forensics experts. They need to know exactly what was compromised and if any weak spots remain. The chance that an insider was involved makes the case even harder to solve. Trust in internal controls is at stake.
ATNS notified that its internal technical team has already implemented containment measures and removed the malicious software, but for a full determination of the attack source, compromise scope, and residual risks, independent digital forensics is required.
Impatto sull'infrastruttura critica e risposta regionale
This breach comes as ransomware attacks on aviation infrastructure are rising fast. Dark Reading reports a sixfold jump in ransomware incidents in the sector in 2025. African critical infrastructure is now a prime target. Grounded flights and broken operations draw attention. The OT systems hit in this breach run on specialized embedded hardware. Many use old firmware and custom networking protocols. That makes patching and response much harder than in regular IT setups.
Experts quoted in the report say weak security governance, skill gaps, and poor system upkeep are common in the region. These problems likely played a role in the breach. The ATNS case follows a pattern seen in other big ransomware attacks. In our reported earlier on the Columbus ransomware breach, slow detection and weak internal controls made things worse. The lesson is clear.
Governance e prospettive per la sicurezza
The ATNS investigation should reveal how the breach started, how far it spread, and what risks remain for aviation safety and data. This case shows why strong security governance and constant system upkeep are urgent. In sectors where OT links directly to public safety and global travel, there is no room for weak controls. Italian rules enforced by AGCOM require strict security and incident reporting for critical infrastructure. These standards matter worldwide. They help prevent and limit damage from attacks like this.
ATNS's breach sends a blunt warning to all critical infrastructure operators. Stopping the attack is just the start. Without a culture of proactive security, tough oversight, and investment in cyber skills, even the most vital networks stay exposed. External and internal threats both matter. The aviation sector is global. Cybersecurity cannot be an afterthought. This breach should spark real change-not just in South Africa, but everywhere that manages critical airspace.