
Tecniche di Cyberattacco e Tipologie di Minaccia
133 articoliIl confine con le aree vicine resta concreto: la tecnica va usata come soggetto specifico dell'articolo, non come etichetta generica per qualsiasi incidente di sicurezza. La categoria privilegia caratteristiche strutturali e relazioni tecniche, evitando dati temporanei.
KiteWorks ordina lo spegnimento globale dei server per fermare un attacco zero day
KiteWorks ha imposto a tutti i clienti nel mondo di spegnere i server per sei ore sabato, tentando di bloccare un attacco zero day imminente contro le sue piattaforme di comunicazione sicura.
Nova ransomware traced to real identity after global victim surge
Nova ransomware, born from the RALord group, has spread fast and hit victims worldwide. Investigators have now tied the operation to a specific person using digital clues and breach data, revealing the real face behind the attacks.
Storm-2570 breaks into global networks using remote access tools
Storm-2570 isn't tied to just one ransomware group. It moves between Qilin, DragonForce, Anubis, and BERT, always using the same set of remote access and data theft tools. Microsoft shows how this affiliate keeps breaking in-and what defenders need to do to stop them.
PAYLOAD ransomware turns Active Directory into a weapon
The PAYLOAD ransomware group has flipped the script, using Microsoft Active Directory Group Policy to freeze Windows systems and steal data-without dropping classic ransomware.
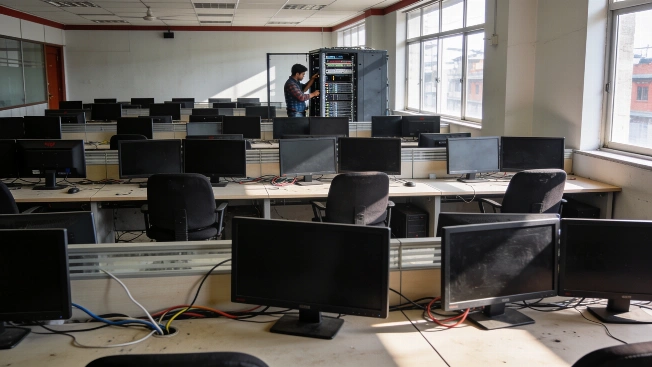
Ransomware attack shuts down Nepal Stock Exchange
A ransomware hit on Data Hub has stopped trading for 72 stockbrokers, forcing NEPSE to freeze the market and raising urgent questions about the safety of Nepal's financial data systems.
Disputa su assicurazione ransomware: il tribunale dell'Illinois svela le ambiguità delle polizze
Un attacco ransomware da 4,89 milioni di dollari ha acceso una battaglia legale a Chicago: il giudice ha escluso la compagnia assicurativa, ma il produttore resta nel mirino per la poca chiarezza della polizza.
Kiteworks spenta in tutto il mondo dopo allerta zero-day federale
Un allarme lanciato dai servizi di intelligence federali ha imposto a Kiteworks la chiusura preventiva dei sistemi in tutto il mondo. Nessuna patch e nessun CVE: le organizzazioni restano in attesa, con dati sensibili bloccati e nessuna certezza sulla sicurezza.
Ransomware strikes Bright Smile Dental Care in Fishers
Bright Smile Dental Care in Fishers has suffered a ransomware attack that compromised patient records and critical software. While the clinic claims the risk to patients is low, sensitive personal data may have been exposed and affected individuals are being notified.
NetScaler zero-day attacks expose critical flaws in enterprise security
Citrix has confirmed active exploitation of two critical zero-day vulnerabilities in NetScaler ADC and Gateway appliances, both scoring 9.5 CVSS and affecting default configurations. Enterprises face immediate risk, with Citrix and CISA urging rapid patching and forensic checks.
Tre falle zero-day su ViewSonic vCast espongono le lavagne digitali
Tre vulnerabilità zero-day in ViewSonic vCast permettono a chiunque sia sulla stessa rete di spiare gli schermi delle ViewBoard e installare app Android dannose. Nessuna patch disponibile, rischio elevato per scuole e aziende.
NFM Lending hit by huge data breach claim after Interlock ransomware attack
A ransomware group says it stole over 2.5 terabytes of data from NFM Lending, including Social Security numbers and financial records. The breach has triggered a class action lawsuit and urgent questions about the lender's cybersecurity.
Galago ransomware rivendica legami con Panzer: nel mirino la sanità islandese
Galago, gruppo ransomware appena emerso, dichiara una collaborazione con Panzer e punta la sanità islandese. Ma dietro i proclami, mancano prove di attacchi concreti e di una vera partnership.
Ransomware recovery costs surge for schools and universities
Schools and universities now face average recovery bills of $2.26 million after ransomware attacks. Identity breaches and long downtimes are exposing deep weaknesses across the education sector.
Ransomware hits new highs as cybercriminals ramp up attacks in 2026
August 2026 set a new record for ransomware attacks, with more than 1,000 organizations worldwide hit. Factories, hospitals, and IT companies took the brunt as groups like Qilin and The Gentlemen stepped up their campaigns.
Check Point in crisi: attacchi zero-day colpiscono i server di gestione
Check Point lancia patch urgenti dopo che una falla zero-day nei suoi Management Server viene sfruttata in attacchi reali. Le aziende e le agenzie federali hanno solo tre giorni per mettere in sicurezza i sistemi.
Nepal Stock Exchange reopens after ransomware halts trading
Trading at NEPSE came roaring back after a ransomware attack forced a rare shutdown. With systems restored, turnover hit NRs 7.05 billion as regulators pressed for answers on the breach.
ShinyHunters hijacks Clop ransomware leak site in cybercriminal turf war
ShinyHunters has breached and defaced the Clop ransomware gang's dark-web leak site, claiming to have stolen sensitive server data and threatening to extort its rival. The attack exposes vulnerabilities even among top cybercrime groups.
Namibian Defence Force listed in ransomware claim, but evidence is missing
RansomHouse has named the Namibian Defence Force as a victim on its dark web site, but so far, no proof of a breach or stolen data has surfaced. Security researchers say the claim remains unverified and lacks technical evidence.
Settra ransomware colpisce aziende tramite VPN compromesse
Il ransomware Settra prende di mira organizzazioni sfruttando credenziali VPN rubate e strumenti di monitoraggio remoto. Gli attacchi hanno interessato aziende dei settori retail e manifatturiero, con tecniche pensate per eludere le difese e cancellare le tracce.
Ransomware agentico: il primo attacco AI senza operatori umani
Per la prima volta, un ransomware gestito da agenti AI autonomi ha condotto un'intera campagna di estorsione senza intervento umano, accelerando le intrusioni e rendendo il crimine informatico più accessibile e scalabile.
Ransomware paralyses South African organisations as recovery costs climb
South African organisations are under constant attack from ransomware, with most incidents traced to stolen credentials and poor security. Even as more companies use backups, recovery is slow and expensive, according to the 2026 Sophos report.
Hostinger blocca un attacco zero-day su LiteSpeed Web Server
Un attacco zero-day ha colpito un server Hostinger in Brasile sfruttando una falla critica di LiteSpeed Web Server. L'azienda ha bloccato l'intrusione, collaborato con il fornitore per la patch e rafforzato le difese contro minacce AI-driven.
MUIS: No mass data leak after ransomware hits mosque payroll system
Singapore's Islamic Religious Council says no large-scale data theft occurred after a ransomware attack on the SmartHRMS payroll system. Data was recovered, operations continued, and no ransom was paid.
cups2root: lpadmin diventa root su Ubuntu senza ostacoli
cups2root è un nuovo exploit che permette a chi ha accesso lpadmin su Ubuntu di ottenere una shell root sfruttando una catena di vulnerabilità CUPS. Non ci sono patch disponibili e le difese standard non bastano.
Ransomware surges in the Middle East as AI gives hackers new power
Ransomware attacks have jumped twenty-fold in the Middle East, with AI-driven hacking tools now targeting critical infrastructure and major economies. Both criminal and state-backed groups are reshaping the region's cyber threat landscape.
Cartrack sotto indagine dopo un attacco ransomware che espone i dati dei clienti
Ad agosto, un attacco ransomware ha colpito Cartrack, esponendo dati personali e bancari dei clienti. L'Information Regulator ha aperto un'indagine per chiarire la portata della fuga di informazioni e le responsabilità dell'azienda.
Ransomware blocca i servizi al Nipigon District Memorial Hospital
Un attacco ransomware ha colpito il Nipigon District Memorial Hospital, bloccando i sistemi informatici e costringendo la struttura a sospendere alcuni servizi essenziali. I pazienti si trovano ad affrontare attese più lunghe e incertezza sulla sicurezza dei dati personali.
Zero-day flaw in TP-Link Tapo C200 exposed homes to surveillance
A zero-day vulnerability in TP-Link Tapo C200 cameras let attackers bypass authentication and access live video. Patches have been released, but a third critical flaw is still under review, raising new concerns for connected home security.
Ransomware gangs escalate attacks on Gulf infrastructure
A wave of ransomware attacks is battering Gulf businesses and critical infrastructure, as criminal groups shift focus to the Middle East and leverage AI to amplify their reach. New data reveals a dramatic spike in incidents and exposes the vulnerabilities putting entire sectors at risk.
Ransomware exploits VMware vCenter flaw before patches are applied
Ransomware groups are taking advantage of a critical VMware vCenter vulnerability just days after a patch was released, encrypting ESXi virtual machines and highlighting how little time defenders have to respond.
Ransomware attack halts payroll for Singapore mosques
A ransomware attack has shut down the payroll and HR system used by Singapore's Islamic Religious Council, exposing staff data but leaving public services running. Authorities and provider Avelogic are investigating and working to restore security.
Ransomware recovery targets collapse for nearly all companies
Fenix24's new report reveals that almost every company fails to meet its own ransomware recovery targets, with identity management and backup systems routinely sabotaging efforts to restore operations within days.
Zero trust blocks ransomware threats for older adults and critical systems
Ransomware attacks now threaten hospitals and critical infrastructure, putting lives at risk. Experts explain why zero trust is essential for older adults, families, and organizations facing constant digital threats.
Sandworm and Qilin breach Cisco Firewall Manager in coordinated attack
Russian military hackers and the Qilin ransomware collective have simultaneously compromised Cisco Secure Firewall Management Center, using authentication bypass and hardcoded credentials to seize control of entire enterprise firewall fleets and exfiltrate sensitive data.
Harley-Davidson named in CL0P ransomware extortion attempt
The CL0P ransomware group has listed Harley-Davidson as a target, threatening to leak data allegedly stolen from the company. Harley-Davidson has not confirmed any breach, and there is no independent evidence that data was accessed or stolen.
Pagina 1 di 5